New Research from ISACA Reveals That Organizations with Unfilled Cybersecurity Roles Suffer More Attacks
New Research from ISACA Reveals That Organizations with Unfilled Cybersecurity Roles Suffer More Attacks
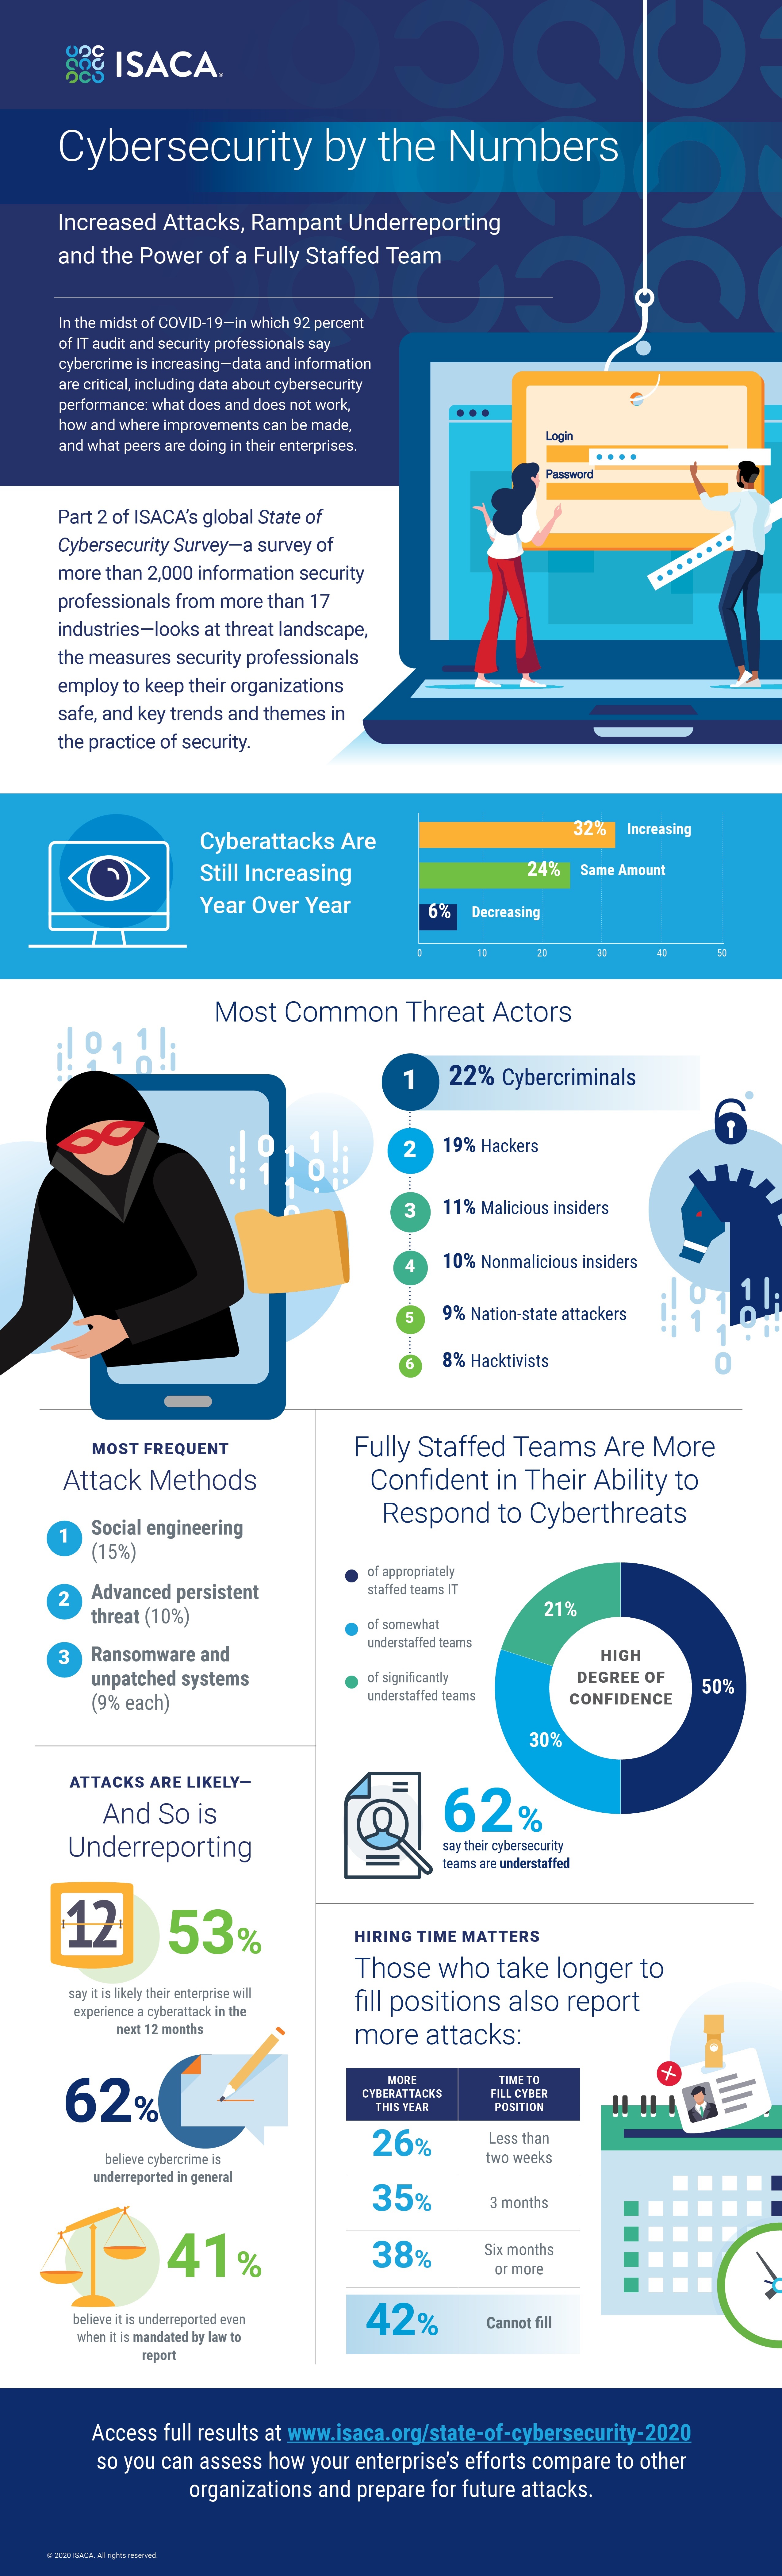
Part 2 of ISACA’s global State of Cybersecurity Survey—a survey of more than 2,000 information security professionals from more than 17 industries—looks at threat landscape, the measures security professionals employ to keep their organizations safe, and key trends and themes in the practice of security. (Graphic: Business Wire)
SCHAUMBURG, Ill.--(BUSINESS WIRE)--The cybersecurity landscape is constantly evolving, and even more so during this time of disruption. According to ISACA’s State of Cybersecurity 2020 Survey Part 2 report, most respondents believe that their enterprise will be hit by a cyberattack soon—with 53 percent believing it is likely they will experience one in the next 12 months. This and other survey findings provide a powerful snapshot of what cybersecurity professionals face—including types of cyberattacks, solutions, and reporting challenges—and just how much of an impact cyber teams make on their organizations’ security.
The survey found cyberattacks are also continuing to increase, with 32 percent of respondents reporting an increase in the number of attacks relative to a year ago. However, there is a glimmer of hope—the rate at which the attacks increase is continuing to decline over time; last year, just over 39 percent of respondents answered in the same way.
Though while attacks are going up—with the top attack types reported as social engineering (15 percent), advanced persistent threat (10 percent) and ransomware and unpatched systems (9 percent each)—respondents believe that cybercrime remains underreported. Sixty-two percent of professionals believe that enterprises are failing to report cybercrimes, even when they have a legal or contractual obligation to do so.
“These survey results confirm what many cybersecurity professionals have known from for some time and in particular during this health crisis—that attacks have been increasing and are likely to impact their enterprise in the near term,” says Ed Moyle, founding partner, Security Curve, and lead writer of the report. “It also reveals some hard truths our profession needs to face around the need for greater transparency and communication around these attacks.”
Among the tools used in security programs for fighting these attacks are artificial intelligence (AI) and machine learning solutions, and the survey asked about these for the first time this year. While these options are available to incorporate into security solutions, only 30 percent of those surveyed use these tools as a direct part of their operations capability.
The survey also found that while the number of respondents indicating they are significantly understaffed fell by seven percentage points from last year, a majority of organizations (62 percent) remain understaffed. Understaffed security teams and those struggling to bring on new staff are less confident in their ability to respond to threats. Only 21 percent of “significantly understaffed” respondents report that they are completely or very confident in their organization’s ability to respond to threats, whereas those who indicated their enterprise was “appropriately staffed” have a 50 percent confidence level. The impact goes even further, with the research finding that enterprises struggling to fill roles experience more attacks, with the length of time it takes to hire being a factor. For example, 35 percent of respondents in enterprises taking three months to hire reported an increase in attacks and 38 percent from those taking six months or more. Additionally, 42 percent of organizations that are unable to fill open security positions are experiencing more attacks this year.
“Security controls come down to three things—people, process and technology—and this research spotlights just how essential people are to a cybersecurity team,” says Sandy Silk, CISSP, Director of IT Security Education & Consulting, Harvard University, and ISACA cybersecurity expert. “It is evident that cybersecurity hiring and retention can have a very real impact on the security of enterprises. Cybersecurity teams need to think differently about talent, including seeking non-traditional candidates with diverse educational levels and experience.”
To read the full report, expert insights and related resources, visit: www.isaca.org/state-of-cybersecurity-2020. Find additional cybersecurity resources at www.isaca.org/training-and-events/cybersecurity.
About ISACA
For more than 50 years, ISACA® (www.isaca.org) has advanced the best talent, expertise and learning in technology. ISACA is a global professional association and learning organization that leverages the expertise of its 145,000 members who work in information security, governance, assurance, risk and privacy to drive innovation through technology. It has a presence in 188 countries, including 223 chapters worldwide.
Contacts
Emily Van Camp, evcamp@isaca.org, +1.847.385.7223